OpenCode Confirms Breach After Users Report Stolen API Keys and Unauthorized AI Bills

OpenCode has confirmed an OpenCode breach that may have exposed third-party API keys stored in its workspaces, with some users reporting unauthorized charges on their Anthropic, OpenAI and Google accounts. The company said the incident stemmed from unauthorized access to a legacy system that was already being decommissioned.
Which keys were exposed, and who was affected
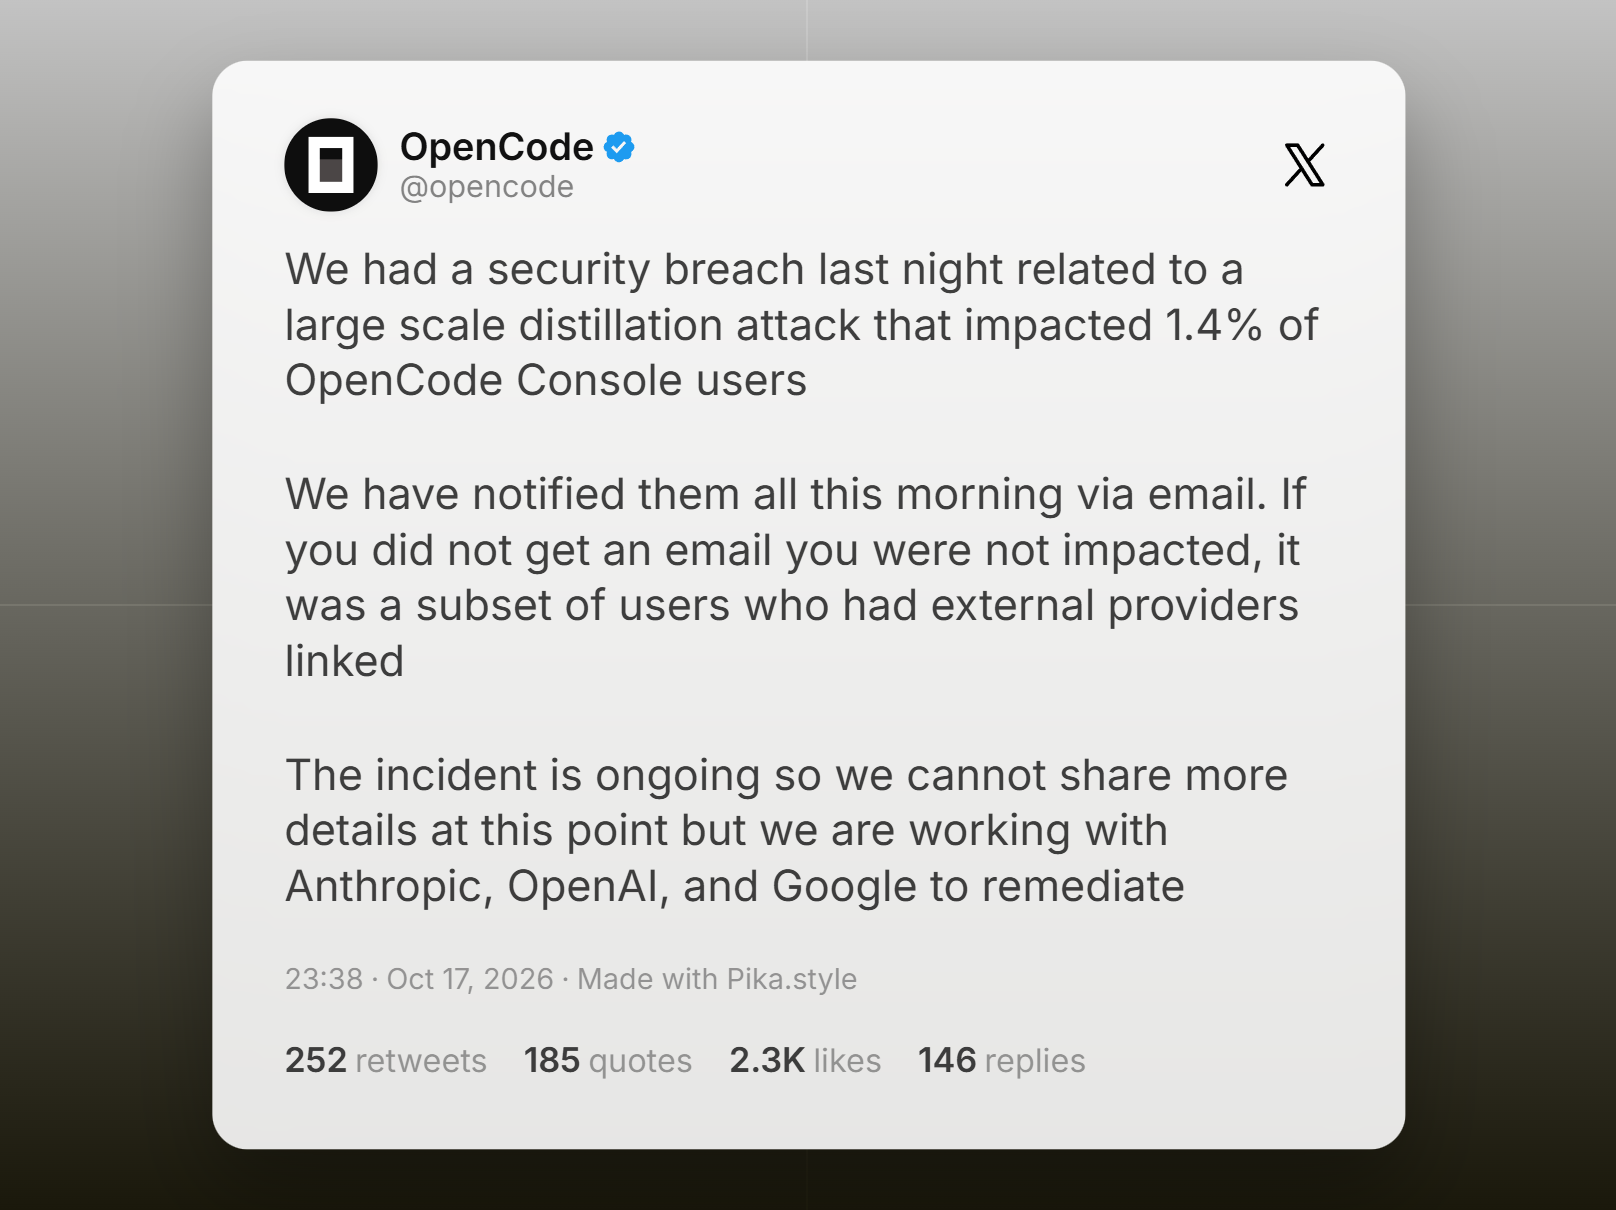
The exposed credentials include OpenAI and Anthropic keys, according to OpenCode. Those keys allow requests to be billed to the account holder, which explains why the fallout has appeared as unexpected spending rather than a direct loss from OpenCode itself.
OpenCode estimates that 1.4% of Console users are affected. The company described the group as a subset of users who had linked external providers to their accounts. All affected users were notified by email, OpenCode said, and anyone who did not receive a notification was not impacted.
Users report bills and suspended projects
Reports of unauthorized activity surfaced on Reddit and X before OpenCode’s notice reached users. One Reddit user cited $400 in unauthorized charges on an Anthropic account. Another reported roughly €200 in Google usage charges, along with a Google project suspension for excessive abuse. A commenter said OpenAI and Anthropic usage alerts arrived before OpenCode’s message.
Those figures are individual accounts, not a total. The full financial extent of the incident has not been disclosed.
Distillation attack link and provider coordination
OpenCode tied the breach to a large-scale distillation attack, a technique in which model responses are collected to train another model. The company said the incident is still ongoing and that it is working with Anthropic, OpenAI and Google. Whether the distillation attack originated from the breach has not been established.
What affected users should do
OpenCode asked affected users to revoke and replace their provider keys, update any applications that rely on those keys, and review recent usage for unexpected activity. Users who received no email notification do not need to take action on the basis of this incident.
Access problems continue
Some users have reported separate access issues. Several said their OpenCode service API keys had expired, while others encountered social login failures through Google or GitHub, with an error reading “Unable to start social login.” One user said a replacement key worked only after several attempts; another said the new key still did not work.
OpenCode has not provided an exact count of affected users, the date of the breach, or a timeline for resolution.



1 comment